02/29/24
- API
- Workato - bot for HR it is what is telling Sailpoint that someone has been terminated
- Sailpoint
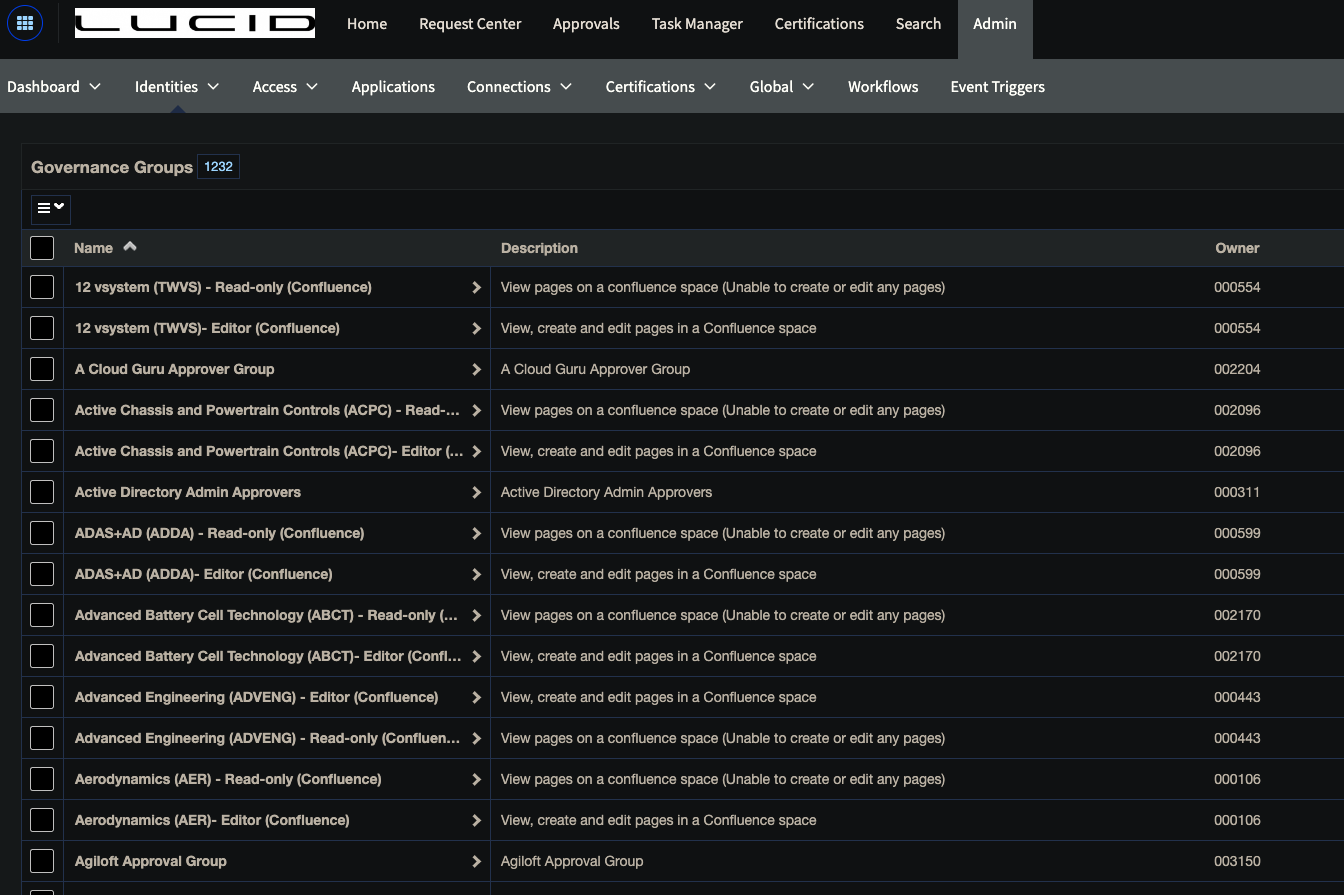
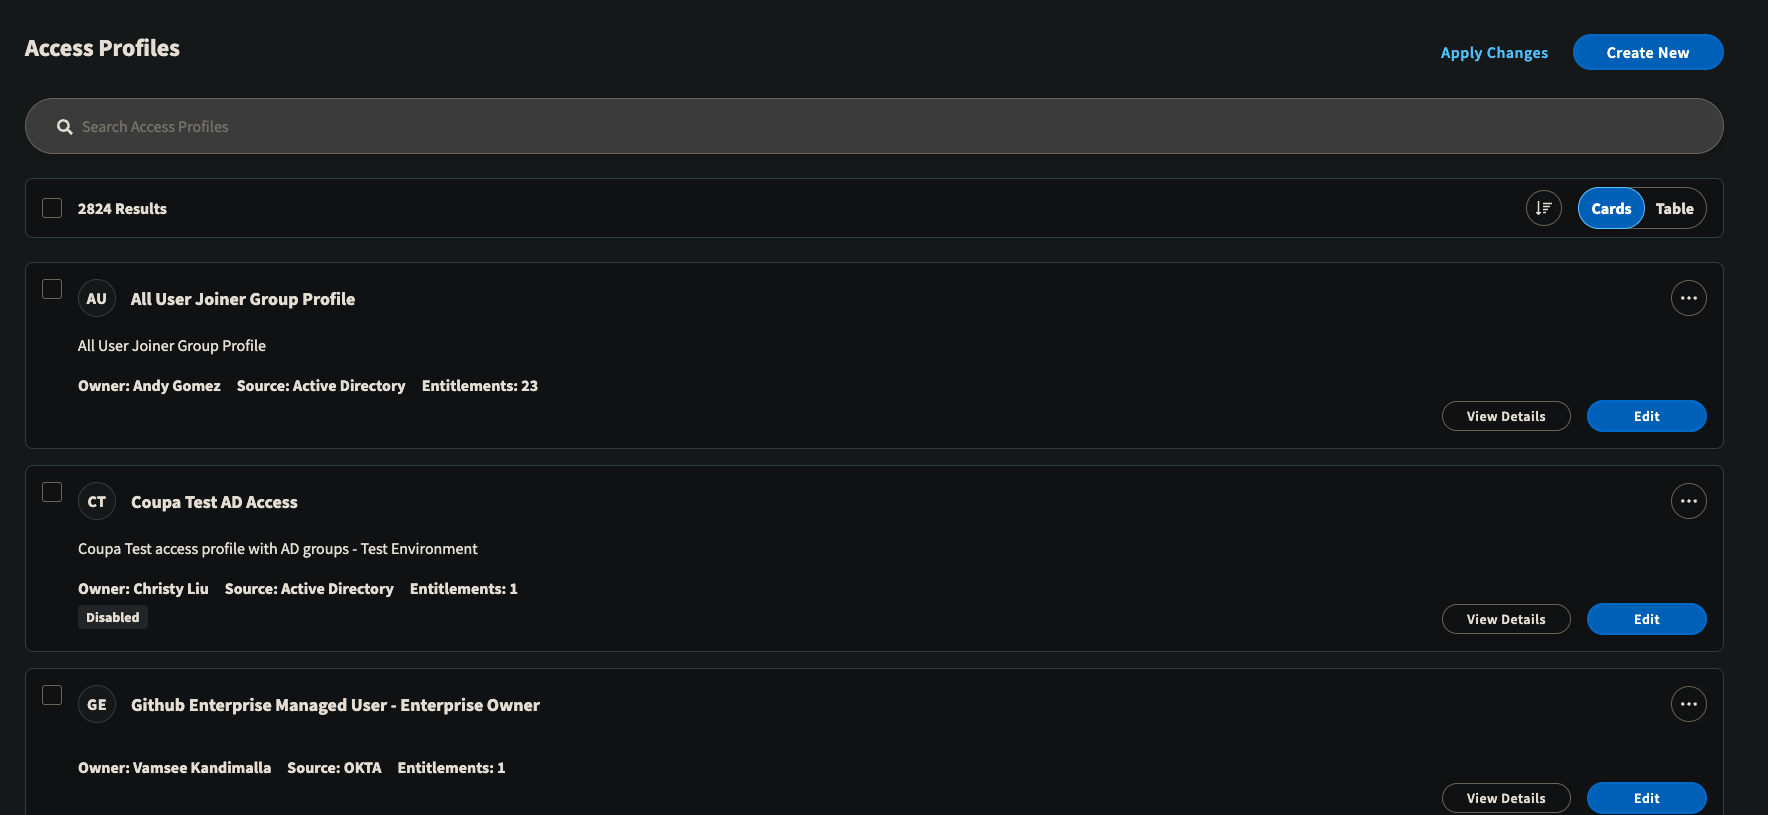
- Governance groups - are the main groups or the applications that entitlement and access profiles fall under
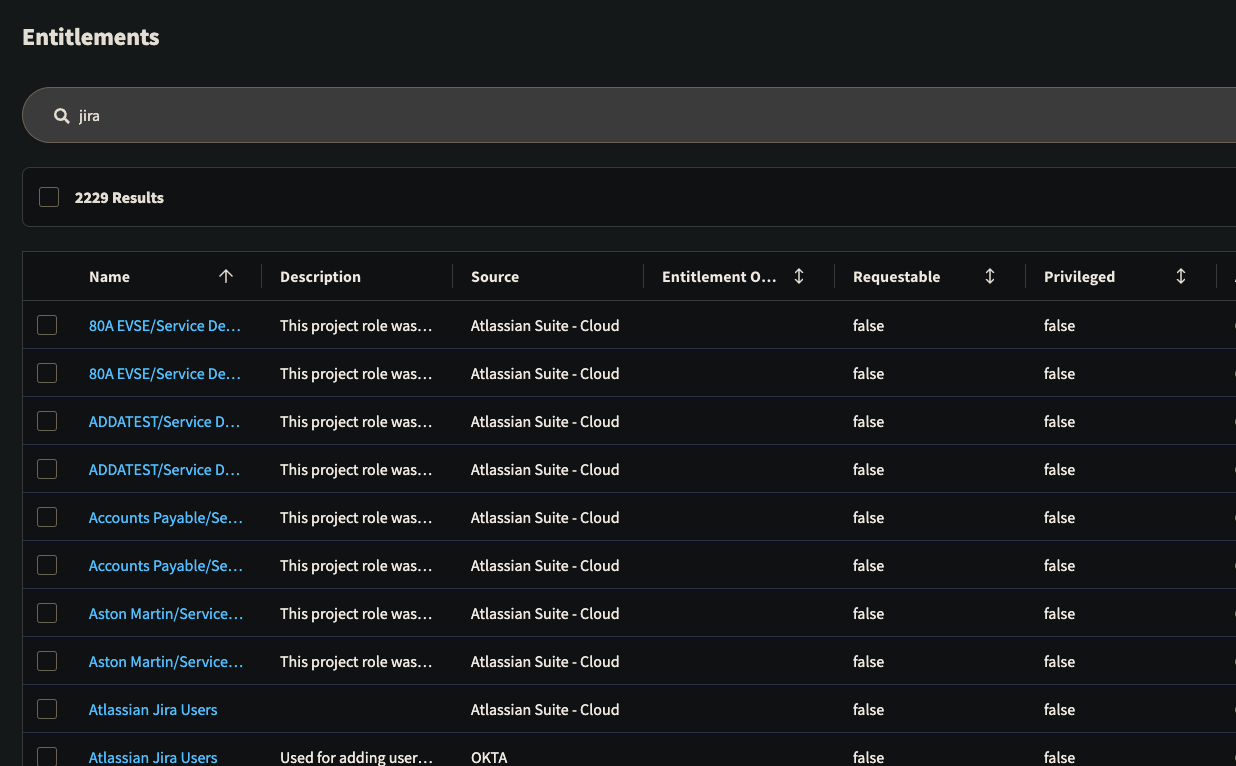
Entitlement - An account within an application for axample Jira is the account the entitlement would be a jira project within that application
Access profiles - Are the View Only, Edit Only or Developer Only type of roles. Different type of access within the application
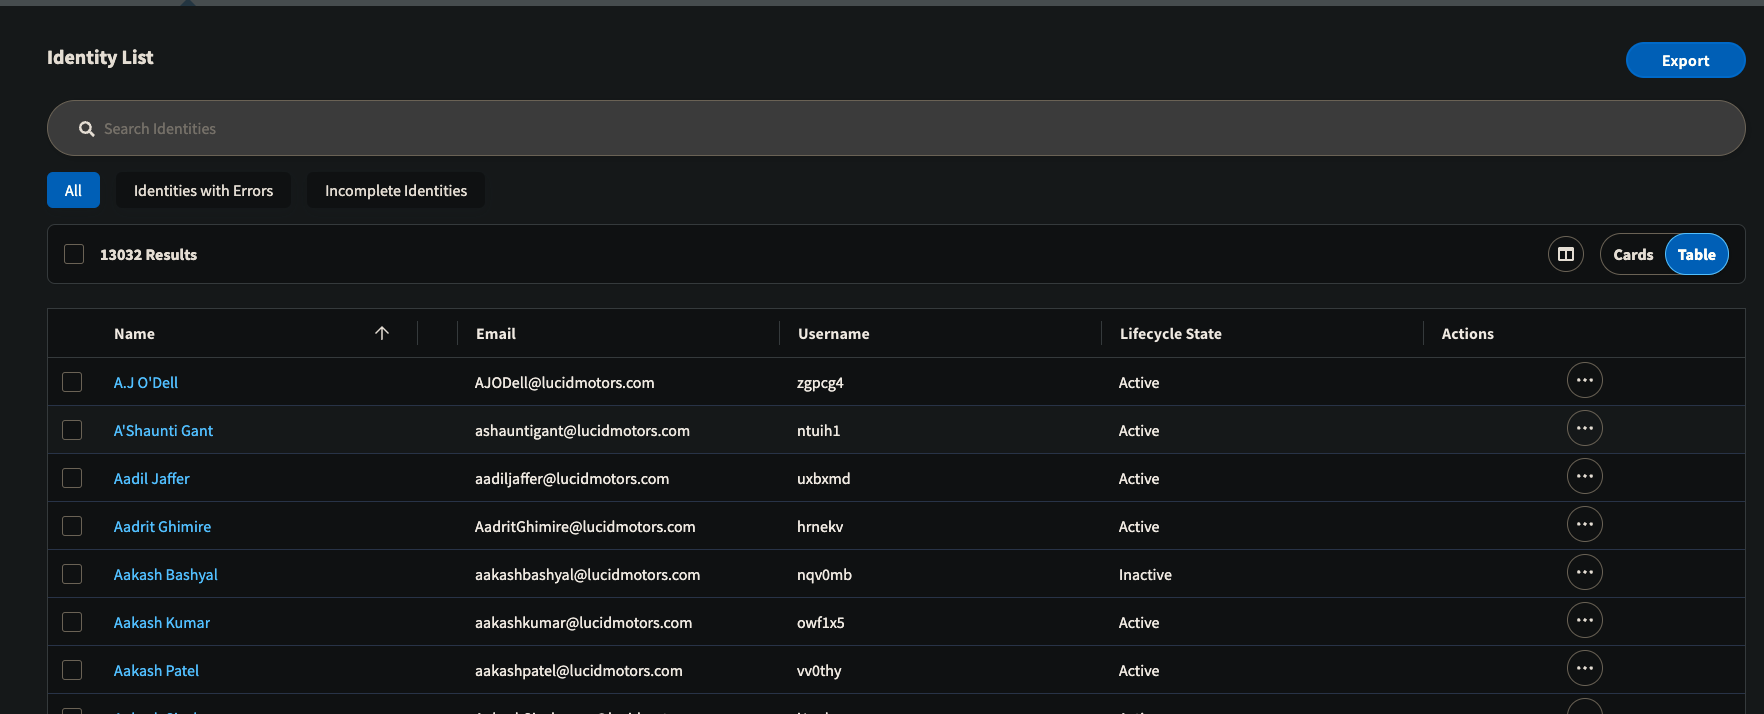
Identity List - The user’s account
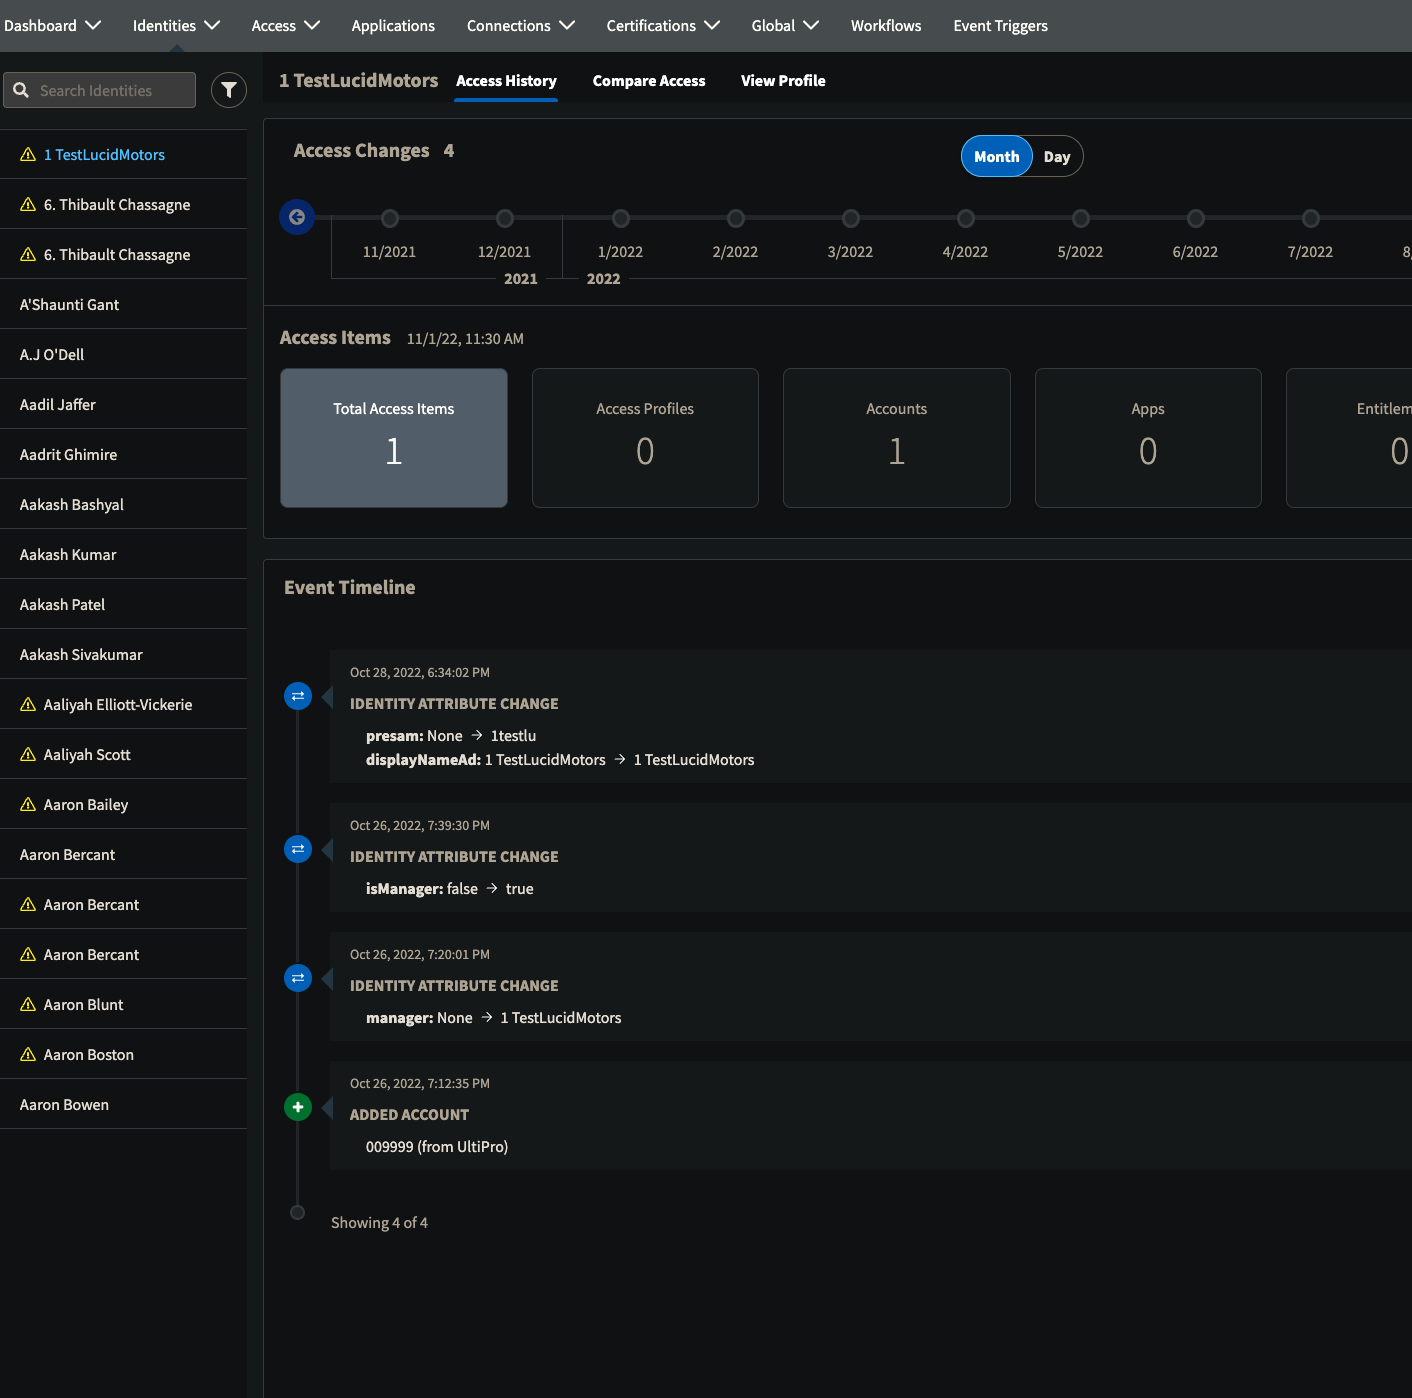
Access History - what you accessed and what you removed
- Can’t access Sailpoint - It is usually showing an error with a key, for some reason the user had two accounts in Sailpoint which one being inactive and Sailpoint does not know which account to use
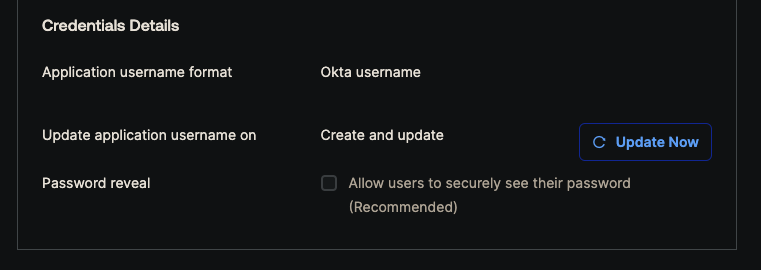
- Directory Integration to active directory - AD and Okta
- If the group is made in AD the group will then sync every hour to Okta and show up in Okta
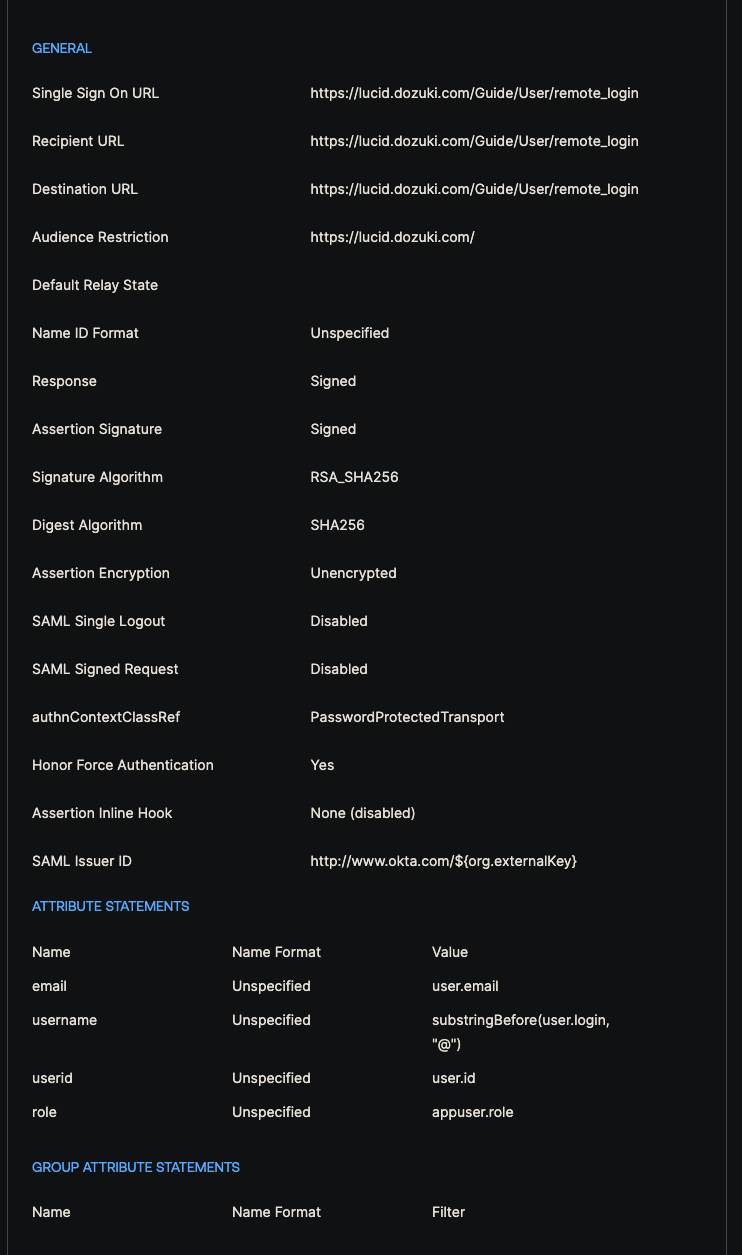
- Some apps require URLS to be pointed to and also require what typer of
- If the group is made in AD the group will then sync every hour to Okta and show up in Okta
- Some applications have both Okta group and AD group with name sp_ which is used for Sailpoint verification
- SAML response - SAML Tracer checks what account Okta is sending to the application then we need check what account the application receives