Furry
---
rs
Self-described “gay furry hackers” on July 2 breached archival data from a site that was operated by the Heritage Foundation until recently, and on Tuesday released two gigabytes of internal data originally collected by the conservative think tank. Now an executive director at the influential organization is so hopping mad that he might as well invest in a kangaroo costume.
The hacktivist collective, SiegedSec, has been engaged in a campaign called “OpTransRights,” in which it targets government websites with the aim of disrupting efforts to enact or enforce anti-trans and anti-abortion laws. Heritage Foundation was selected due to its Project 2025 plans, seen as a blueprint for Donald Trump to reshape the U.S. with sweeping far-right reforms should he win another term as president, SiegedSec told CyberScoop on Tuesday. Group member “vio” informed the outlet that they aimed to provide “transparency to the public regarding who exactly is supporting” Heritage, and that the leaked data included “full names, email addresses, passwords, and usernames” of individuals linked to the nonprofit.
This material, as the Daily Dotreported and as the Heritage Foundation now confirms, came from the Daily Signal, Heritage’s media and commentary site, which lists one Mike Howell as an investigative columnist. The former Trump administration official in the Department of Homeland Security is also the executive director of Heritage’s Oversight Project, an initiative focused on border security, elections, and countering the “influence” of the Communist Party of China. It was Howell who contacted SiegedSec in the wake of the breach to get answers about their motivations — and as he continued to message “vio,” his texts grew more unhinged and threatening.
After declining to talk with Howell by phone, vio described what it was that they and their hacker furry comrades sought to accomplish: “[W]e want to make a message and shine light on who exactly supports the [H]eritage foundation,” they wrote. “[W]e [don’t] want anything more than that, not money and not fame. [W]e’re strongly against Project 2025 and everything the [H]eritage foundation stands for.” Howell seemed stunned by the explanation. “That’s why you hacked us?” he replied. “Just for that?” (Once the full chat log was released by SiegedSec, Howell confirmed to the Daily Dot that it was genuine, and that the conversation had taken place on Wednesday.)
From there, Howell’s tone shifted. “We are in the process of identifying and outing [sic] members of your group,” he wrote. “Reputations and lives will be destroyed. Closeted Furries will be presented to the world for the degenerate perverts they are.” As vio expressed skepticism that anyone in SiegedSec would be identified and continued to criticize the Heritage agenda as harmful to human rights, Howell invoked Biblical authority and seethed that the hackers had “turned against nature.”
“God created nature, and nature’s laws are vicious. It is why you have to put on a perverted animal costume to satisfy your sexual deviances,” Howell wrote. “Are you aware that you won’t be able to wear a furry tiger costume when you’re getting pounded in the ass in the federal prison I put you in next year?” When vio taunted the executive for this outburst and hinted that they would be posting the conversation online, Howell replied, “Please share widely. I hope the word spreads as fast as the STDs do in your degenerate furry community.”
He went on to liken furry culture to bestiality, which he called a “sin,” prompting vio to ask him, “whats ur opinion on vore.” (Vorarephilia, or vore, is a fetish typically expressed in erotic art of people or creatures eating one another.) A Twitter user shared a screenshot of this exchange Wednesday afternoon, leading Howell to quote-tweet the post with lyrics from rapper Eminem‘s 2000 single “The Way I Am.”
Hours later, Howell learned through the Daily Dot‘s reporting that vio had decided to try to quit their life of cybercrime, and that the rest of the collective agreed it was “time to let SiegedSec rest for good,” in part to avoid FBI attention. “COMPLETE AND TOTAL VICTORY,” Howell tweeted. “I have forced the Gay Furry Hackers to DISBAND.”
Related
### How a Trump Win Would Threaten Access to Birth Control and Emergency Contraception
### Project 2025 Architect Bragged About Killing Dog With A Shovel: Report
But it remains to be seen whether these hackers — who last year managed to breach NATO systems as well as a major U.S. nuclear lab that they demanded begin research on “creating IRL catgirls” — will truly disappear into the shadows. Like an empowering fursona, hacking can be an identity that’s hard to give up. Before he congratulates himself any more, Howell might want to at least change his passwords.
Update July 11, 3:50 p.m.: After publication, the Heritage Foundation sent Rolling Stone a statement clarifying that the site was not operated by the think tank, and disputing that they were hacked. The story has been updated to reflect this, and the full statement can be found below:*}:
“The Heritage Foundation was not hacked. An organized group stumbled upon a two-year-old archive of The Daily Signal website that was available on a public-facing website owned by a contractor. The information obtained was limited to usernames, names, email addresses, and incomplete password information of both Heritage and non-Heritage content contributors, as well as article comments and the IP address of the commenter. No Heritage systems were breached at any time, and all Heritage databases and websites remain secure, including Project 2025. The data at issue has been taken down, and additional security steps have since been taken as a precaution. The story of a ‘hack’ is a false narrative and exaggeration by a group of criminal trolls trying to get attention.”
---
tnr
Project 2025 Creator Threatens “Gay Furry” Hackers in Disturbing Texts
After “Gay Furry” hackers breached the think tank behind the extreme Project 2025 agenda, its executive director is spewing venom.
Participants in the 2022 Eurofurence in Berlin
Self-described “gay furry hackers” behind a group dubbed SiegedSec on Wednesday released text exchanges between Heritage Foundation executive Mike Howell and a member of the hacker group. The texts followed a leak of nearly two gigabytes of data from The Daily Signal, the Heritage Foundation’s blog site.
In the texts, Howell appears apoplectically humorless, oscillating between threats to expose the hackers and hopes for violence against them. Howell is a columnist for The Daily Signal, the site whose subscriber data SiegedSec leaked amid a spree of other leaks. The hacked data included the “full names, email addresses, passwords, and usernames” of people associating with the Heritage Foundation, one spokesperson of the gay furry hacktivists said, in order to shed “transparency to the public regarding who exactly is supporting” the conservative think tank.
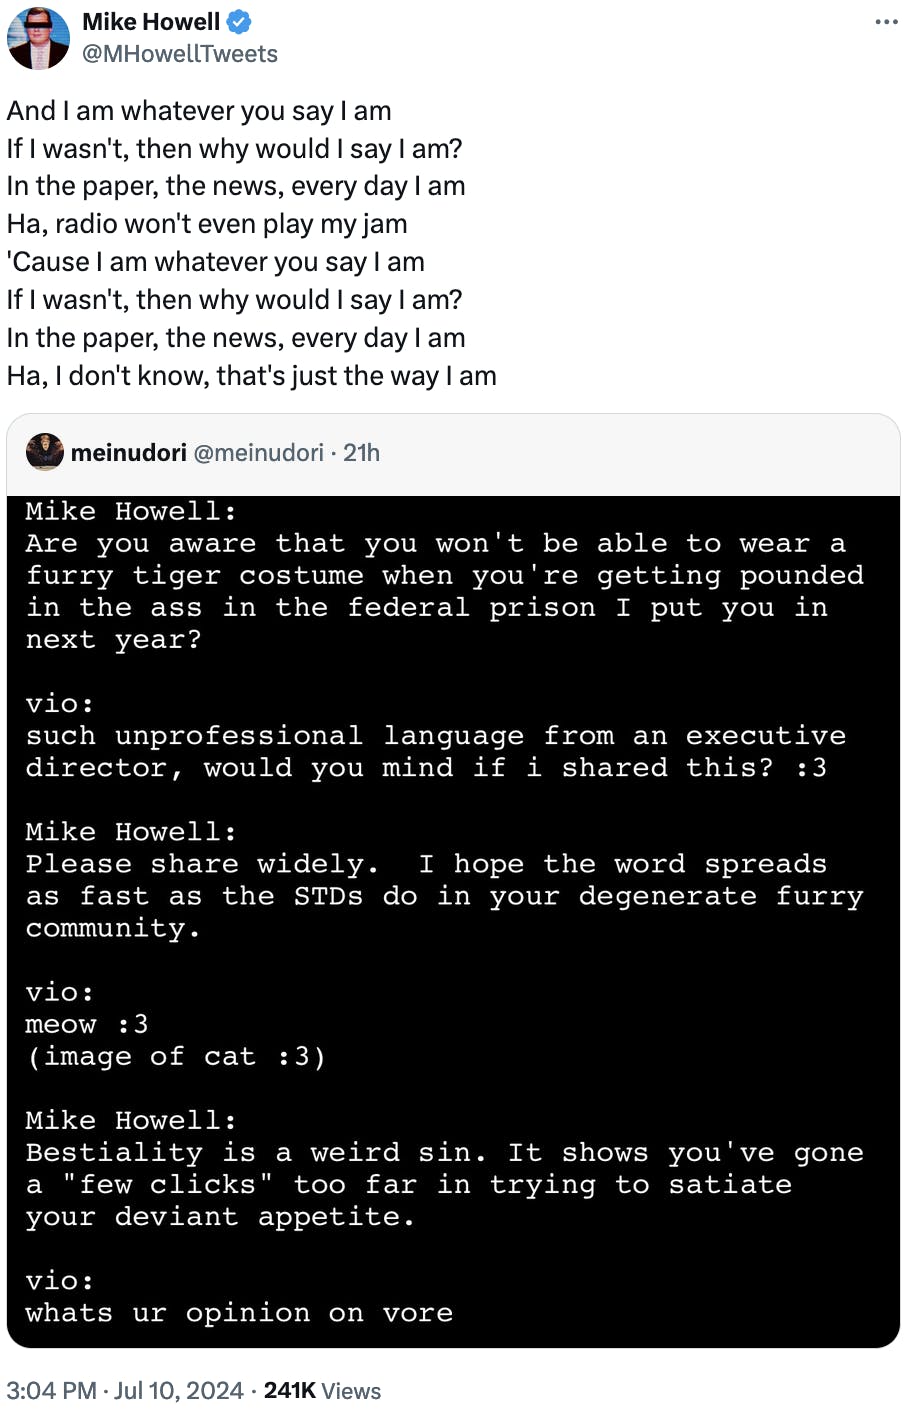
“Are you aware that you won’t be able to wear a furry tiger costume when you’re getting pounded in the ass in the federal prison I put you in next year?” Howell asked a member of SiegedSec who identified themselves as “vio.”
“Please share widely,” Howell told the hacker group after they asked if they could release their text exchanges with Howell. “I hope the word spreads as fast as the STDs do in your degenerate furry community.”
“meow :3” vio responded.
“Bestiality is a weird sin. It shows you’ve gone a “few clicks” too far in trying to satiate your deviant appetite,” Howell continued.
Vio cheekily replied, “whats ur opinion on vore.” Howell elevated the text exchange, which he confirmed to the DailyDot as authentic, by posting lyrics to Eminem’s “The Way I Am.”
During their conversation, Howell promised to reveal the identity of the hackers, declaring, “Closeted Furries will be presented to the world for the degenerate perverts they are.” This proved unintimidating, as vio reassured him none of their members would be identified and that their hack is small potatoes compared to the Heritage Foundation’s aspirations. “the rights your org violates will be 10x worse than any crime ive committed,” vio told Howell. “you do not follow god if you use religion as a crutch to hate people. while i hide behind a screen to fight for my rights, you hide behind religion to attack the rights of others.”
Following the release of the text exchanges, Howell took to X (formerly Twitter) to falsely accuse someone reviewing the leak of being involved. Howell also declared “complete and total victory” that he “forced the Gay Furry Hackers to DISBAND” after the group posted that their Heritage hack would be their last. SiegedSec has claimed credit for over two years of hacktivism against far-right sites, as well as hacking NATO, twice, and a nuclear lab to demand it create catgirls.
SiegedSec stated they hacked the Heritage Foundation’s Daily Signal in rejection of Project 2025, which they describe as “an authoritarian Christian nationalist plan to reform the United States government.” The hack is part of the group’s campaign against anti-trans organizations and websites dubbed #OpTransRights. While claiming the Heritage hack would be their last, SiegedSec also stated that in addition to releasing their texts with Howell, they “have an extra surprise for him coming soon.”
---
---
vid has pix of IP
16 Jul 2024,
Heritage Foundation insists it was not hacked by ‘gay furries’
Quote:
A group of self-proclaimed “gay furry hackers” says it breached the Heritage Foundation earlier this month, releasing two gigabytes of the right-wing think tank’s internal data on Tuesday. On its Telegram channel, the hacktivist collective SiegedSec — which has previously claimed responsibility for hacking NATO’s computer systems — said the Heritage hack was part of its #OpTransRights campaign, which also targeted the far-right media outlet Real America’s Voice and the Hillsong megachurch. The group also cited their objections to Project 2025, the Heritage Foundation’s policy proposal for a second term for former President Donald Trump, as a motivating factor.
In an email to The Verge, Heritage Foundation spokesperson Noah Weinrich denied that Heritage had been hacked, calling it a “false narrative and an exaggeration by a group of criminal trolls trying to get attention.”
“An organized group stumbled upon a two-year-old archive of The Daily Signal website that was available on a public-facing website owned by a contractor,” Weinrich said in an emailed statement. “The information obtained was limited to usernames, names, email addresses, and incomplete password information of both Heritage and non-Heritage content contributors, as well as article comments and the IP address of the commenter. No Heritage systems were breached at any time, and all Heritage databases and websites remain secure, including Project 2025. The data at issue has been taken down, and additional security steps have since been taken as a precaution.”
The Heritage Foundation claims the alleged hack was an exaggeration for attention, but in the meantime, Mike Howell, the executive director of the foundation’s Oversight Project, has triumphantly taken credit for disbanding “the Gay Furry Hackers.”
SiegedSec has released chat logs of a conversation one of its members claimed to have with Howell on Signal. The chat logs show a person who claims to be Howell asking a SiegedSec member why the group hacked the Heritage Foundation and threatening to expose the hackers.
Quote:
We are in the process of identifying and outting members of your group
Reputations and lives will be destroyed
Closeted Furries will be presented to the world for the degenerate perverts they are
You cannot hide Your means are miniscule compared to mine. You now can either turn yourself in or you can cooperate
Howell confirmed the legitimacy of the messages in an X exchange with a Daily Dot reporter.
Weinrich did not comment on the alleged messages between Howell and SiegedSec.
The messages also show Howell claiming to be “tied up with the fbi issuing a 2702 order” on SiegedSec’s social media. SiegedSec has indeed disbanded, a decision its members attribute to their “own mental health, the stress of mass publicity, and to avoid the eye of the FBI.”
A SiegedSec representative who goes by vio told The Verge they “completely expected” Heritage to deny that it had been hacked. “Many companies try denial to save face,” vio said. “The server we hacked was linked to The Daily Signal, and the server was named ‘first-heritage-foundation’. Clearly, Heritage was genuinely hacked.”
“Mike’s threats and insults showed anger that confirmed what Heritage denied,” vio said.
In a statement on Telegram, SiegedSec said the goal of the hack was to draw attention to — and combat — the Heritage Foundation’s anti-LGBT and anti-abortion policy proposals.
“The Heritage Foundation is a conservative think tank in America, among the most influential public policy organizations,” one SiegedSec member wrote on Telegram. “This organization is responsible for leading Project 2025, an authoritarian Christian nationalist plan to reform the United States government.” The hacked data, which was reviewed by CyberScoop, includes Heritage Foundation blogs and material related to The Daily Signal, a news website affiliated with the organization.
Heritage published Project 2025, its sweeping recommendations for a second Trump term, in April 2023, with a “broad coalition” of more than 100 other conservative organizations. The 900-plus-page “mandate for leadership” touches on virtually every sector of the executive branch, from the White House to the bevy of federal agencies under the president’s control.
Broadly speaking, its recommendations involve expanding presidential power, purging federal agencies of career employees, and replacing them with Trump loyalists. The mandate calls for dismantling entire federal departments — including the departments of Commerce, Education, and Homeland Security, the latter of which would be replaced with a new agency that is more extreme in its mission and less subject to oversight. Project 2025 also urges Trump to reverse the Food and Drug Administration’s approval of abortion pills, eliminate policies that promote “abortion as health care,” outlaw pornography, and shut down “telecommunications and technology firms that facilitate its spread.”
The mandate’s chapter on the Federal Communications Commission — written by Brendan Carr, the agency’s head under Trump — calls for the imposition of “transparency rules on Big Tech” and an overhaul of Section 230 of the Communications Decency Act, the law that states that “interactive computer services” can’t be treated as the publishers or speakers of third-party content published on their platforms. Carr claims that Section 230 allows tech companies to “censor protected speech,” echoing claims that major social media companies suppress right-wing viewpoints.
Trump recently attempted to distance himself from Project 2025, claiming he has “no idea” who is behind the plan — even though a CNN analysis found that more than 140 former members of his administration were involved in drafting the mandate.
Hacktivists release two gigabytes of Heritage Foundation data
Quote:
An established cybercrime group with a track record of attacking political targets posted on Tuesday roughly two gigabytes of data from the Heritage Foundation, a prominent conservative think tank based in Washington, D.C.
Self-described “gay furry hackers,” SiegedSec said it released the data in response to Heritage Foundation’s Project 2025, a set of proposals that aim to give Donald Trump a set of ready-made policies to implement if he wins this fall’s election. Its authors describe it as an initiative “to lay the groundwork for a White House more friendly to the right.”
The data, reviewed by CyberScoop, includes Heritage Foundation blogs and material related to The Daily Signal, a right-wing media site affiliated with Heritage. The data was created between 2007 and November 2022.
The group says it gained access to the data on July 2 and released it to provide “transparency to the public regarding who exactly is supporting heritage (sic),” a spokesperson for the group who goes by the online handle “vio” told CyberScoop in an online chat Tuesday.
The data includes the “full names, email addresses, passwords, and usernames” of people associating with Heritage, vio said, including users with U.S. government email addresses. “This itself can have an impact to heritage’s (sic) reputation,” they added, “and it’ll especially push away users in positions of power.”
A Heritage spokesperson told CyberScoop after publication that the organization was not “hacked.” Instead, the spokesperson said “an organized group stumbled upon a two-year-old archive of The Daily Signal website that was available on a public-facing website owned by a contractor. The information obtained was limited to usernames, names, email addresses, and incomplete password information of both Heritage and non-Heritage contributors, as well as article comments and the IP address of the commentor.”
No Heritage systems were breached at any time, the spokesperson said, and the story of a hack “is a false narrative and an exaggeration by a group of criminal trolls trying to get attention.”
SiegedSec also claimed to be in possession of more than 200 gigabytes of additional “mostly useless” data, which the group said won’t be released.
The attack was carried out as part of SiegedSec’s “OpTransRights,” campaign, which has previously included the defacement of government websites and data theft from states either considering or implementing anti-abortion or anti-trans legislation.
The Heritage Foundation did not respond to a request for comment Tuesday. The attack marks the second suffered by Heritage this year. In April, a Heritage official told Politico that the think tank had shut down its network in response to a breach by a nation-state hacking group.
Democrats have sought to tie Trump to Project 2025 proposals as an example of what to expect from his second term. Heritage President Kevin Roberts made news last week when he said the American right was “in the process of the second American Revolution, which will remain bloodless if the left allows it to be.”
SiegedSec, which emerged on Telegram in April 2022, has also targeted various NATO portals, the city of Fort Worth and a company involved in the monitoring of offshore oil and gas facilities.
Heritage Foundation Exec Threatens ‘Gay Furry Hackers’ in Unhinged Texts
Quote:
Self-described “gay furry hackers” on July 2 breached archival data from a site that was operated by the Heritage Foundation until recently, and on Tuesday released two gigabytes of internal data originally collected by the conservative think tank. Now an executive director at the influential organization is so hopping mad that he might as well invest in a kangaroo costume.
The hacktivist collective, SiegedSec, has been engaged in a campaign called “OpTransRights,” in which it targets government websites with the aim of disrupting efforts to enact or enforce anti-trans and anti-abortion laws. Heritage Foundation was selected due to its Project 2025 plans, seen as a blueprint for Donald Trump to reshape the U.S. with sweeping far-right reforms should he win another term as president, SiegedSec told CyberScoop on Tuesday. Group member “vio” informed the outlet that they aimed to provide “transparency to the public regarding who exactly is supporting” Heritage, and that the leaked data included “full names, email addresses, passwords, and usernames” of individuals linked to the nonprofit.
This material, as the Daily Dot reported and as the Heritage Foundation now confirms, came from the Daily Signal, Heritage’s media and commentary site, which lists one Mike Howell as an investigative columnist. The former Trump administration official in the Department of Homeland Security is also the executive director of Heritage’s Oversight Project, an initiative focused on border security, elections, and countering the “influence” of the Communist Party of China. It was Howell who contacted SiegedSec in the wake of the breach to get answers about their motivations — and as he continued to message “vio,” his texts grew more unhinged and threatening.
After declining to talk with Howell by phone, vio described what it was that they and their hacker furry comrades sought to accomplish: “We want to make a message and shine light on who exactly supports the Heritage foundation,” they wrote. “We don’t want anything more than that, not money and not fame. We’re strongly against Project 2025 and everything the Heritage foundation stands for.” Howell seemed stunned by the explanation. “That’s why you hacked us?” he replied. “Just for that?” (Once the full chat log was released by SiegedSec, Howell confirmed to the Daily Dot that it was genuine, and that the conversation had taken place on Wednesday.)
From there, Howell’s tone shifted. “We are in the process of identifying and outing [sic] members of your group,” he wrote. “Reputations and lives will be destroyed. Closeted Furries will be presented to the world for the degenerate perverts they are.” As vio expressed skepticism that anyone in SiegedSec would be identified and continued to criticize the Heritage agenda as harmful to human rights, Howell invoked Biblical authority and seethed that the hackers had “turned against nature.”
“God created nature, and nature’s laws are vicious. It is why you have to put on a perverted animal costume to satisfy your sexual deviances,” Howell wrote. “Are you aware that you won’t be able to wear a furry tiger costume when you’re getting pounded in the ass in the federal prison I put you in next year?” When vio taunted the executive for this outburst and hinted that they would be posting the conversation online, Howell replied, “Please share widely. I hope the word spreads as fast as the STDs do in your degenerate furry community.”
He went on to liken furry culture to bestiality, which he called a “sin,” prompting vio to ask him, “whats ur opinion on vore.” (Vorarephilia, or vore, is a fetish typically expressed in erotic art of people or creatures eating one another.) A Twitter user shared a screenshot of this exchange Wednesday afternoon, leading Howell to quote-tweet the post with lyrics from rapper Eminem‘s 2000 single “The Way I Am.”
Hours later, Howell learned through the Daily Dot‘s reporting that vio had decided to try to quit their life of cybercrime, and that the rest of the collective agreed it was “time to let SiegedSec rest for good,” in part to avoid FBI attention. “COMPLETE AND TOTAL VICTORY,” Howell tweeted. “I have forced the Gay Furry Hackers to DISBAND.”
But it remains to be seen whether these hackers — who last year managed to breach NATO systems as well as a major U.S. nuclear lab that they demanded begin research on “creating IRL catgirls” — will truly disappear into the shadows. Like an empowering fursona, hacking can be an identity that’s hard to give up. Before he congratulates himself any more, Howell might want to at least change his passwords.
Update July 11, 3:50 p.m.: After publication, the Heritage Foundation sent Rolling Stone a statement clarifying that the site was not operated by the think tank, and disputing that they were hacked. The story has been updated to reflect this, and the full statement can be found below:
“The Heritage Foundation was not hacked. An organized group stumbled upon a two-year-old archive of The Daily Signal website that was available on a public-facing website owned by a contractor. The information obtained was limited to usernames, names, email addresses, and incomplete password information of both Heritage and non-Heritage content contributors, as well as article comments and the IP address of the commenter. No Heritage systems were breached at any time, and all Heritage databases and websites remain secure, including Project 2025. The data at issue has been taken down, and additional security steps have since been taken as a precaution. The story of a ‘hack’ is a false narrative and exaggeration by a group of criminal trolls trying to get attention.”
---
Project 2025 co-author spotted in photo with friend in drag
Project 2025 co-author Mike Howell accused of hypocrisy after photo emerges with friend in drag (exclusive)
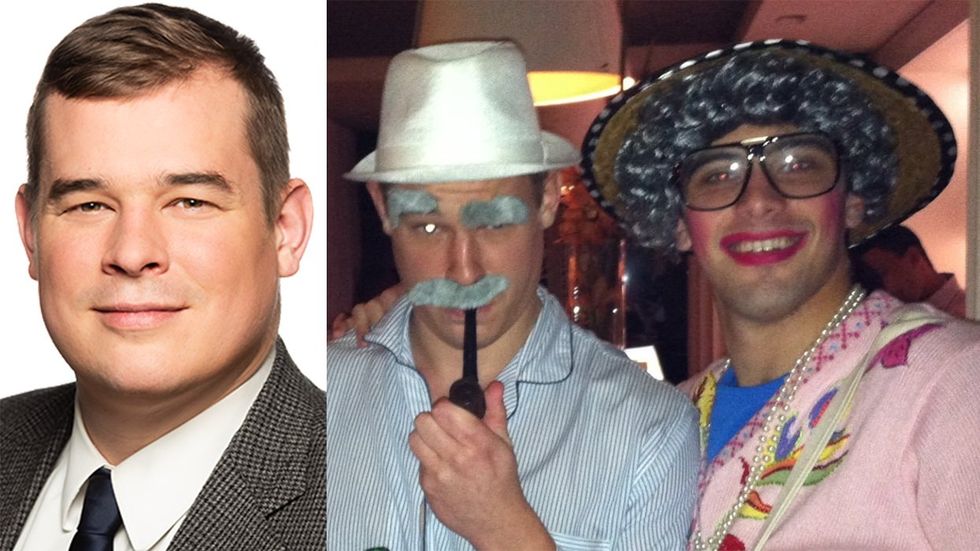
Courtesy The Heritage Foundation; yelp.com user Fern M., Atlanta GA
Howell has condemned drag before. He confirmed to The Advocate that the photo is authentic.
:{July 26 2024
A prominent operative for the ultra-conservative Heritage Foundation and a co-author of theRepublicanProject 2025 agenda that the organization’s president, Kevin D. Roberts, has said aims to “institutionalize Trumpism” across the government, is being called a hypocrite after The Advocate discovered a photo of him with a friend dressed indrag.
The photo, posted on Yelp on December 12, 2012, and captioned “The good doctor with his lost wife,” shows a younger Mike Howell, Heritage’s executive director of the Oversight Project, smiling alongside a friend in full drag attire. According toEsquire, the Oversight Project is Heritage’s oversight initiative that targets the Biden administration. The initiative, led by Howell, focuses on developing data to support controversial claims and investigations. The project has come under scrutiny for its dubious methods and significant financial investments in efforts to undermine political opponents. Esquire reports that the Oversight Project has even insinuated that the FBI and the Biden administration were involved in the assassination attempt on former President Donald Trump.
Howell’s enjoyment of men in women’s clothes starkly contrasts with his public condemnations of drag culture and theLGBTQ+ community. Howell has been a vocal critic of drag queens and an outspoken opponent oftransgender rights and LGBTQ+ rights broadly. His public statements and aggressive actions, including targeting drag queen story hours and asserting that drag culture is harmful to children, make this revelation particularly striking.
For instance, Howell has harshly criticized events like Drag Queen Story Hours, where drag performers read to children in libraries and other community spaces. He has repeatedly voiced concerns about exposing children to drag culture, arguing it is inappropriate and damaging. On social media, Howell has not held back his disdain. On April 25, he posted on X (formerly Twitter): “As the disputed winner of the 2005 election for student president of West Potomac, and with the power that vests in me, I officially condemn on behalf of all Wolverines. It was much easier when it was just MS-13 gang fights. Don’t need the trans sex stuff.”
In another tweet on March 21, Howell remarked: “These are not man bites dogs stories. These are the norm. Frankly, I wish we cleared a drag queen in one of our investigations.” Such statements underline his consistent position against drag culture and the LGBTQ+ community.
In 2023, Howellwrote critically about a “Drag Story Hour” event hosted byWashington, D.C.’s Martin Luther King Jr. Memorial Library, asserting that drag queens harm children. Howell’s harsh rhetoric targeted organizations like the HRC, which he labeled a “radical LGBTQ group” that is “a major proponent of giving cross-sex hormones to minors, despite science clearly indicating the horrific dangers of this practice.”
---
SiegedSec, short for Sieged Security and commonly self-described as the "Gay Furry Hackers",[1][2] was a black-hat criminal hacktivist group,[3][4][2] that was formed in early 2022, that committed a number of high profile cyber attacks, including attacks on NATO,[3][4][5] Idaho National Laboratory,[1][2] and Real America's Voice.[6][7] On July 10, 2024, after attacking The Heritage Foundation, the group announced that they would be disbanding in an effort to avoid closer scrutiny.[8]
Description
SiegedSec was led by an individual under the alias "vio".[9] Short for "Sieged Security",[10][11][12] SiegedSec's Telegram channel was first created in April 2022,[13] and they commonly referred to themselves as "gay furry hackers".[14][15] SiegedSec has targeted a wide variety of organisations, ranging from intergovernmental organisations like NATO[3][4] and federal research facilities like the Idaho National Laboratory[1][2] to right-wing movements like The Heritage Foundation[16][17] and Real America's Voice,[18] and various U.S. states that have pursued legislative decisions against gender-affirming care.[19]
Notable attacks
Atlassian
On February 14, 2023, major Australian software provider Atlassian had its data leaked on the internet by SiegedSec using stolen employee credentials. 13,000 employee records were affected in this hack, and SiegedSec was also able to obtain floorplans for Atlassian offices.[20]
#OpTransRights movements
:(\s\t\y\l\e=\"\f\o\n\t-\f\a\m\i\l\y:\M\e\r\r\i\w\e\a\t\h\e\r\"):
In June 2023, SiegedSec targeted several United States government entities to protest anti–gender-affirming-care bills. The hackers released a variety of data including data from the Government of Fort Worth Texas, The Nebraska Supreme Court, and South Carolina police files.[19]
In April and May 2024, SiegedSec began their second trans rights operation, #OpTransRights2. The hackers successfully targeted and leaked data from Real America's Voice[6][7] and River Valley Church.[21]
University of Connecticut
:(\s\t\y\l\e=\"\f\o\n\t-\f\a\m\i\l\y:\M\e\r\r\i\w\e\a\t\h\e\r\"):
In July 2023, SiegedSec sent a series of spoof emails to undergraduate University of Connecticut students using LISTSERV, falsely announcing the "Unfortunate Passing of Radenka Maric". During an interview with the Hartford Courant, "vio" claimed responsibility for the incident, explained the vulnerability which allowed for them to perform the hack, and said that they "did it for the lulz".[9]
NATO
:(\s\t\y\l\e=\"\f\o\n\t-\f\a\m\i\l\y:\M\e\r\r\i\w\e\a\t\h\e\r\"):
In 2023, NATO portals were compromised twice by SiegedSec. The leak totalled over 3000 internal documents.[22][3][4][5] The portals compromised were Joint Advanced Distributed Learning, NATO Lessons Learned Portal, Logistics Network Portal, Communities of Interest Cooperation Portal, NATO Investment Division Portal, and NATO Standardization Office.[23] Shortly after the incident, NATO announced that they would be investigating the attack.[24][25]
Bezeq
:(\s\t\y\l\e=\"\f\o\n\t-\f\a\m\i\l\y:\M\e\r\r\i\w\e\a\t\h\e\r\"):
On October 30, 2023, SiegedSec attacked Bezeq, one of the largest Israeli telecommunication providers. The hackers released information on nearly 50,000 customers.[26]
Idaho National Laboratory
:(\s\t\y\l\e=\"\f\o\n\t-\f\a\m\i\l\y:\M\e\r\r\i\w\e\a\t\h\e\r\"):
In November 2023, Idaho National Laboratory's Oracle HR system was compromised leading to the leaking of personal employee data,[27] with the group demanding that the laboratory put research into "creating real-life catgirls" in exchange for the data to be removed.[11] On February 7, 2024, a number of employees received ransom payment requests in the mail with their data.[28]
The Heritage Foundation
In July 2024, SiegedSec announced that they had breached and leaked data from conservative think tank The Heritage Foundation, which has led the Project 2025 proposals. They released a statement on Telegram, calling the proposals "an authoritarian Christian nationalist plan to reform the United States government."[15] A Heritage spokesperson dismissed the attacks as "a false narrative and an exaggeration", stating that all databases, systems and websites remained secure.[29][30] The hacking group released chatlogs of a conversation on Signal between "vio" and Heritage Foundation executive Mike Howell, in which Howell stated that he, in collaboration with the FBI, was "in the process of identifying and outting [sic] members of your group."
Disbandment
After releasing the Heritage Foundation chatlogs, SiegedSec announced that they would be disbanding "for our own mental health, the stress of mass publicity, and to avoid the eye of the FBI."[31]
Investigations
Following the Idaho National Laboratory attack, it was announced that the FBI as well as the Cybersecurity and Infrastructure Security Agency had been contacted to help investigate the incident.[32]
---
ahacking crew with a history of blending politics and criminal activities claimed on Saturday to have “targeted various satellite receivers and industrial control systems around the country, particularly in states banning gender affirming care.”
SiegedSec, a group that emerged publicly on Telegram on April 3, 2022, claimed that part of its most recent attack included “a delicious supply chain attack,” which allowed the group to “control” multiple companies’ “accounts used for monitoring satellite receivers, VSATs, VOIP services, etc.” The companies include Halliburton, Shell, Helix Energy and Oceaneering, the group claimed.
SiegedSec has claimed multiple attacks on organizations, corporations and states. Recently, it has taken aim at states where lawmakers have sought to ban or limit gender affirming care or ban and severely limit access to abortion. Last summer, for instance, the group — which describes its members as “gay furry hackers” — targeted state government agencies in Kentucky and Arkansas over those states’ changes to abortion access. The group has also targeted dozens of other companies around the world with more traditional hack and data theft operations.
The July 1 message also included links to download roughly 40 gigabytes of data stolen from the city of Fort Worth Transportation & Public Works. On June 28, SiegedSec posted what it said were roughly 500,000 files — roughly 180 gigabytes — that purportedly included work orders, employee lists, invoices, police reports, emails between City of Fort Worth employees, camera footage “and lots, lots, lots more!”
SiegedSec seemingly hit multiple satellite receivers: the Trimble netR9 that often comes with security disabled by default or default credentials. An online manual says that the default user and password are “admin” and “password,” respectively. A cursory glance through Shodan.io, a database of publicly accessible IP addresses, shows around 1,374 that are online in the U.S. — although some are honeypots. Those receivers are often used for accurate positioning and not communications, says Ron Fabela, chief technology officer at cybersecurity firm Xona.
Some of those receivers could be used in offshore oil rigs. A screenshot that was among the documents SiegedSec posted to Telegram over the weekend showed a map with points located just off Texas’ Gulf Coast, which has a major concentration offshore oil and gas facilities. Additionally, Helix Energy provides services for the offshore energy industry.
Fabela said that so far any impact from possible SeigedSec activity appears to be limited to monitoring services, but he noted that offshore rigs have multiple positioning and telemetry methods. He noted that as SiegedSec appears only to have deleted the ITC Global portal accounts that might be the limit of their access with those networks.
Marlink Group, which owns ITC Global, could not be reached for comment. A spokesperson for Shell said the company is looking into the claims. Halliburton, Helix Energy and Oceaneering did not respond to a request for comment.
“We targeted a company that supplies satellite-related and other devices called ITC Global,” the group said in response to questions sent by CyberScoop on Monday to an email address announcing the hack. “We have more going on with ITC Global aside from just deleting accounts, however I can’t go into specifics.”
Last week, the group announced a pair of attacks, one on June 23 and one on June 28.
“We have decided to make a message towards the U.S government,” the June 23 message read. “Texas happens to be one of the largest states banning gender affirming care, and for that, we have made Texas our target. [F***] the government.”
The City of Fort Worth said in a June 24 statement that the data involved came from “an internal information system” known as Vueworks that facilitates work orders for the Transportation and Public Works and Property Management departments. There was no indication that any other systems were accessed, the city said.
A message posted to the group’s Telegram channel June 28 announced attacks on the Nebraska Supreme Court, the South Dakota Boards and Commissions website, the Texas State Behavioral Health Executive Council, the South Carolina Criminal Justice Information Services portal and the Pennsylvania Provider Self-Service website.
Agencies in each of the states were investigating the alleged hacks, the Record’s Jonathan Greig reported June 30. Texas, Nebraska and South Dakota have laws or policies banning gender affirming care, while South Carolina is considering a transition ban, according to the Human Rights Campaign.
The Pennsylvania attack gave the group access to more than 15,000 “child care records,” SiegedSec said, “however we will not be leaking any data due to… well its child care.”
“We did not intend to also target states that aren’t part of the push to ban gender affirming care, however one opportunity appeared with the Pennsylvania PSS hack, but that’s the only exclusion,” the email to CyberScoop read. “The targeted states were not opportunistic, we targeted them specifically for the gender affirming care issues.”
SiegedSec members “focus more on the message than the money,” the email read. “Although we mostly consider ourselves more blackhat than hacktivists. Money is not our main goal, most of the time we just want to have fun and destroy stuff.”
---
Gay Furries Allegedly Hack The Heritage Foundation - Metro Weekly
,,,but SiegedSec claims that its members believe one hack in particular led to the suspension of their accounts on X.
Following several months of teasing its social media followers, the group announced that it had obtained data from the Heritage Foundation, and had promised, on its X account, to publish the data on July 10.
“they didnt want us posting the heritage hack tomorrow,” vio wrote on their account.
According to the Daily Dot, SiegedSec leaked about 200 gigabytes of data on their Telegram account, containing information from between 2007 and 2022, focusing primarily around the think tank’s news wing, The Daily Signal.
The data includes commenters’ emails and IP addresses, full names, usernames, and passwords, as well as information about those who posted articles on the site.
Cybersecurity expert Jackie Singh, who reviewed the data from the breach, commented on X that she had “identified very embarrassing data within this dataset,” adding, “Why so many Chinese IP addresses?”
“Sample geolocations from the first 100 IPs (these are sorted ‘low to high’, and many Asia-based netblocks start with the number 1),” Singh added in a thread, following up on the earlier post.
Singh also noted that some suspicious IP addresses of commenters on the Heritage Foundation’s website appear to have come from individuals abroad, including Kathmandu, Nepal, and Hong Kong.
“This breach can help shine light on who exactly is supporting Heritage, and also encourage people to fight against them even more than before,” vio told LGBTQ Nation.“I believe it’s also worth noting, this could help show the amount of support Heritage has that’s provided by malicious users or bots from China.”
SiegedSec claims the majority of leaked data is “mostly useless” information that it will not be releasing, although vio did tell LGBTQ Nationthat the user data “has many people of interest,” including members of the U.S. House of Representatives, federal government employees, and Kevin Roberts, president of Heritage Foundation.
The hack of Heritage was part of a campaign known as #OpTransRights, which targets groups opposed to transgender rights, including the right-wing channel “Real America’s Voice” and a Minnesota church whose pastor has made anti-transgender comments.
The Heritage Foundation was reportedly targeted for its creation of Project 2025, a plan that seeks to reshape the United States government in the mold of modern-day right-wing regimes, with a unitary executive at the top and party loyalists installed into various federal agencies in place of longtime government employees.
Project 2025’s policy reforms include erasing protections for LGBTQ individuals, banning LGBTQ-related information, especially in schools, and the full erasure of transgender identity.
SiegedSec posted a transcript of a chat, conducted on the messaging app Signal, between “vio” and Mike Howell, the executive director of the Heritage Oversight Project, the think tank’s investigative arm. In that exchange, vio revealed that the hack was done due to SiegedSec’s opposition to Project 2025.
Howell allegedly threatened to expose members of the hacktivist group, saying they had “turned against nature.”
“We are in the process of identifying and outting (sic) members of your group,” Howell wrote. “Reputations and lives will be destroyed. Closeted Furries will be presented to the world for the degenerate perverts they are. You cannot hide. Your means are miniscule (sic) compared to mine. You now can either turn yourself in or you can cooperate.”
He threatened to place members of SiegedSec in jail.
“Are you aware that you won’t be able to wear a furry tiger costume when you’re getting pounded in the ass in the federal prison I put you in next year?” he wrote.
When vio asked if it was okay to share the transcript, Howell allegedly wrote, “Please share widely. I hope the word spreads as fast as the STDs do in your degenerate furry community.”
Howell also said he was contacting the FBI issuing a “2702 order” on vio’s social media.
“You aren’t that sneaky for your line of work,” he wrote, providing a screenshot of SiegedSec’s bitcoin wallet’s transactions.
“omg you learned how to look up the public history of my bitcoin address!!! good job pal im proud of you :D” vio responded.
A Heritage Foundation spokesperson released the following statement to Metro Weeklyin an email:
“The Heritage Foundation was not hacked,” the spokesperson wrote. “An organized group stumbled upon a two-year-old archive of The Daily Signal website that was available on a public-facing website owned by a contractor. The information obtained was limited to usernames, names, email addresses, and incomplete password information of both Heritage and non-Heritage content contributors, as well as article comments and the IP address of the commenter.
“No Heritage systems were breached at any time, and all Heritage databases and websites remain secure, including Project 2025. The data at issue has been taken down, and additional security steps have since been taken as a precaution. The story of a ‘hack’ is a false narrative and exaggeration by a group of criminal trolls trying to get attention.”
The Heritage spokesperson did not address questions sent by Metro Weeklyregarding Howell’s chat with vio or his threats to involve the FBI.
SiegedSec has since posted a message on its Telegram channels that it plans to disband, saying they were doing so “for our own mental health, the stress of mass publicity, and to avoid the eye of the FBI.”
“I’ve been considering quitting cybercrime lately, and the other members have agreed its time to let SiegedSec rest for good,” the message reads.
“In the past, I have tried quitting cybercrime a few times, and I’ve always been unable to fully quit. This time, hopefully I am able to stay away from it for my own wellbeing. We may not be a cybercriminal group anymore, but we will always [be] hackers and always fighting for the rights of others.
“Within the past week, we have posted the last of our breaches every day,” the message concludes. “We hope you enjoy all of it :3 We also have a couple more private breaches that have been sent to journalists, they’ll handle the rest from there. The channel, all leaks, and our community’s chats will remain open. Feel free to join.”
---
table
---
Defuse Security's Encrypted Pastebin
top 40
- 1.172.10.38
- 1.172.15.59
- 1.186.48.26
- 1.207.26.87
- 1.23.84.39
- 1.234.27.239
- 1.24.119.19
- 1.251.19.135
- 1.26.102.189
- 1.53.161.195
- 1.55.89.216
- 1.55.95.220
- 1.59.151.107
- 1.61.122.87
- 1.62.83.6
- 1.64.176.95
- 1.64.55.226
- 10.0.0.113
- 10.0.1.62
- 10.0.139.95
- 10.0.255.50
- 10.1.1.74
- 10.1.1.81
- 10.1.80.9
- 10.10.125.10
- 10.10.125.12
- 10.10.125.15
- 10.10.125.20
- 10.10.125.21
- 10.10.125.22
- 10.10.125.254
- 10.10.57.99
- 10.11.80.163
- 10.114.18.215
- 10.120.100.227
- 10.133.62.118
- 10.140.103.152
- 10.15.136.32
- 10.16.51.154
- 10.17.99.179
- 10.170.102.172
---
[### Heritage Foundation Exec Threatens 'Gay Furry Hackers' in ...

Rolling Stone
https://www.rollingstone.com › culture › culture-news](https://www.rollingstone.com/culture/culture-news/heritage-foundation-gay-furry-hackers-texts-1235057421/)
Jul 10, 2024 — Mike Howell of Heritage Foundation went at gay furry hacking collective SiegedSec after data breach motivated by Project 2025.
[### Project 2025 Creator Threatens “Gay Furry” Hackers in ...

The New Republic
https://newrepublic.com › breaking-news](https://newrepublic.com/post/183710/project-2025-heritage-foundation-exec-threatens-gay-furry-hackers-texts)
Jul 11, 2024 — After “Gay Furry” hackers breached the think tank behind the extreme Project 2025 agenda, its executive director is spewing venom.
[### no PLEASE tell me someone else sees it 😭😭😭 mike howell ...

TikTok · madison @ yaptastik
42.6K+ views · 3 months ago](https://www.tiktok.com/@yaptastik/video/7390402248213286186)
“I have forced the Gay Furry Hackers to DISBAND” — Mike Howell of the Heritage Foundation, after his fantasizing remarks and Heritage's ...
[### Mike Howell and The Furries

TikTok
https://www.tiktok.com › Discover](https://www.tiktok.com/discover/mike-howell-and-the-furries)
Sep 16, 2024 — 13.6M posts. Discover videos related to Mike Howell and The Furries on TikTok. See more videos about Fursuit Head Tutorial.
[### Think-Tanked,

Harper's Magazine
https://harpers.org › Articles](https://harpers.org/archive/2024/10/think-tanked-mike-howell/)
From an exchange on Signal between Mike Howell, the executive director of the Oversight Project at the Heritage Foundation, a conservative think tank, ...
[### Mike Howell sounds like he's a closeted furry tbh...

X · Malcoreio
80+ likes · 3 months ago](https://twitter.com/Malcoreio/status/1811482700412518798)
Mike Howell sounds like he's a closeted furry tbh... Kermit None Of My Business GIF. GIF. read image description.
---